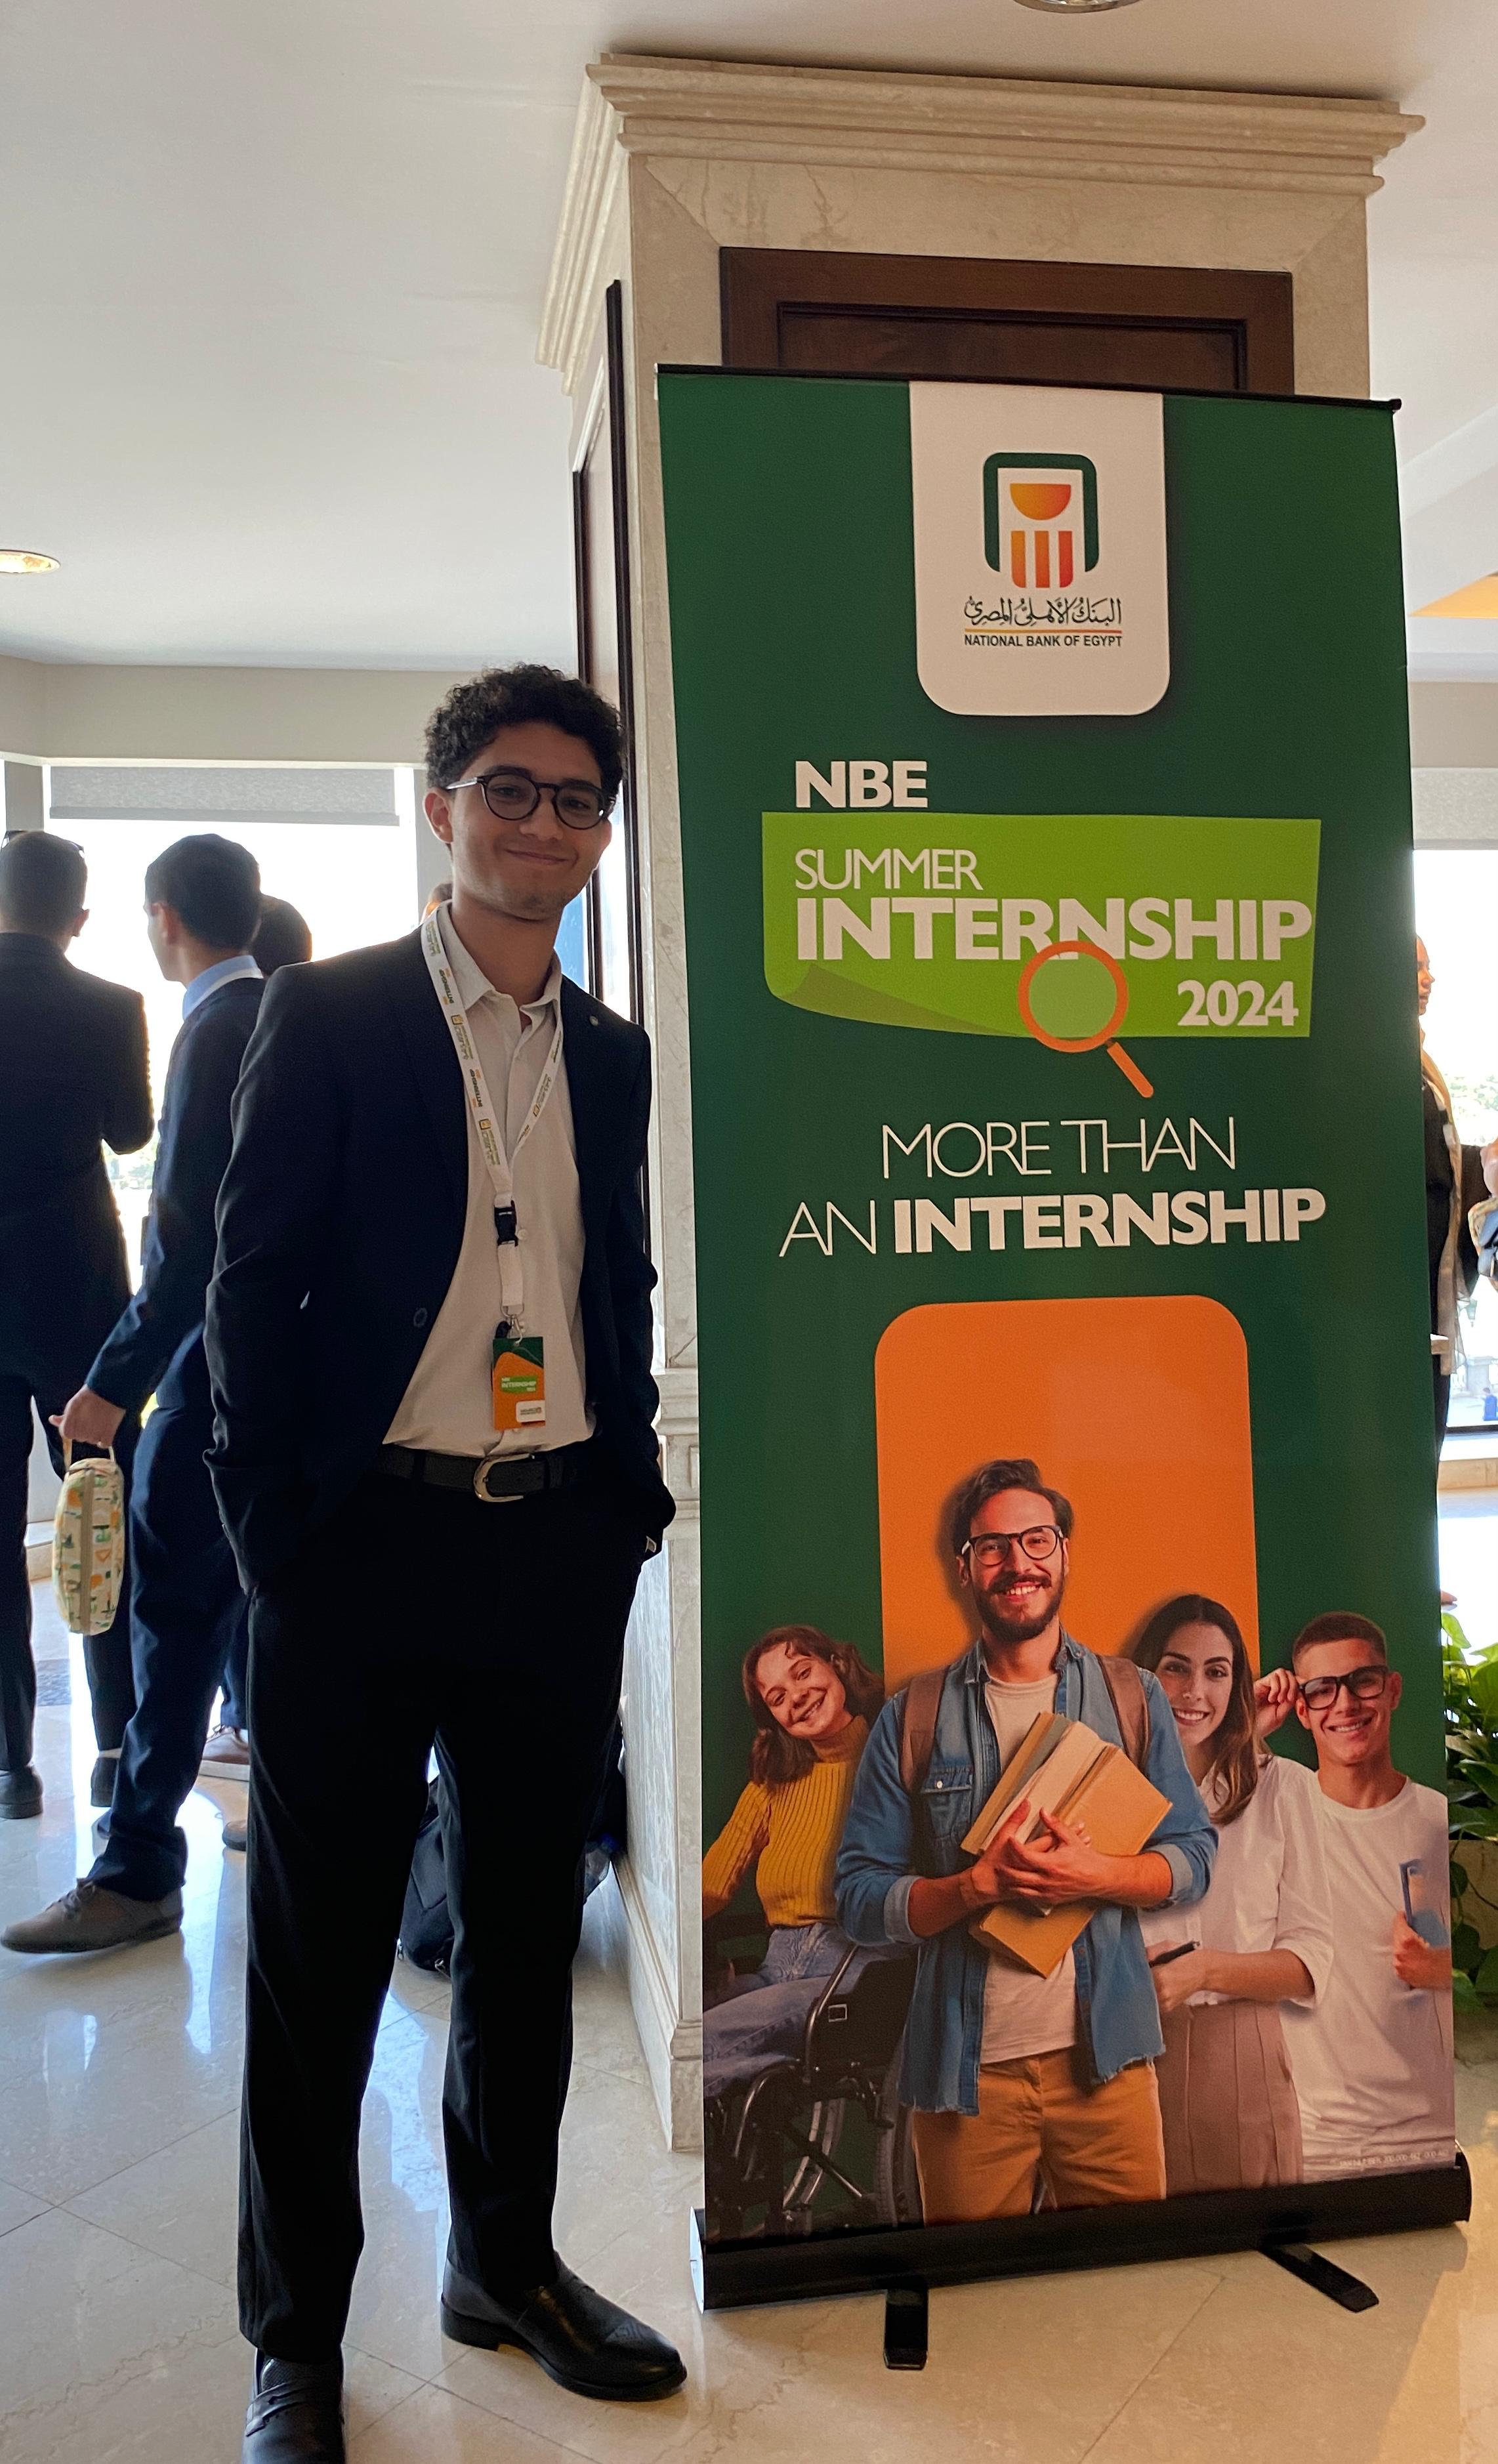
Mohamed Mostafa Ali

Cybersecurity Graduate specializing in SOC Operations, Detection Engineering, and AI Security

Mohamed Mostafa
B.Sc. Computer Science (Cybersecurity), graduated Jun 2026
Arab Academy for Science, Technology & Maritime Transport
GPA: 3.64/4.0 (Excellent with Honors)
Ranked 2nd in the Cybersecurity major
Top 1% TryHackMe (300+ rooms and 40+ badges)

Professional Summary

Cybersecurity graduate with hands-on experience in SOC operations, threat detection, malware analysis, and AI-driven security solutions. Built DroneSentinel – an AI-powered security gap monitoring system – as my graduation project, and completed SecOps and SOC internships including hands-on work with Fortinet SIEM, SOAR, and deception tools at BARQ Systems.

Security Domains

SOC Operations, Incident Response, Detection Engineering, Threat Intelligence, Penetration Testing, Digital Forensics

Technical Skills

Python, Bash, Docker, ELK Stack, Splunk, FortiSIEM, FortiSOAR, ML/AI, Terraform

Experience

Teaching Assistant (AAST), SecOps Intern (BARQ Systems), SOC Analyst Intern (WE Innovate), IT Intern (Juhayna, NBE), Intern (CIB)

Open to SOC Analyst, Detection Engineering, and Incident Response roles, where I can apply my skills and contribute to innovative cybersecurity solutions.
Experience

Teaching Assistant (TA)

Sep 2026 – Present

Arab Academy for Science, Technology & Maritime Transport, Smart Village, Egypt (Part-time, On-site)

  • Assist in delivering Computer Networks labs and tutorials, guiding students through hands-on exercises in IP addressing, subnetting, routing, and switching

Information Technology Intern

Sep 2026

Juhayna Food Industries, Giza, Egypt (Internship, On-site)

  • Worked on IT infrastructure and networking operations while gaining hands-on experience with SAP and ERP systems and understanding their role in enterprise business processes

SecOps Intern

Feb 2026 – Mar 2026

BARQ Systems, Cairo, Egypt (Internship, On-site)

  • Gained hands-on SOC Engineering experience with Fortinet solutions (FortiSIEM, FortiSOAR, FortiDeceptor), developing skills in threat detection, incident response, and security orchestration within a professional SOC environment

SOC Analyst Intern

Aug 2025 – Sep 2025

WE Innovate Bootcamp, Giza, Egypt (Internship, Hybrid)

  • Completed hands-on SOC training: AD setup, Bash scripting, NFS config, Nginx security, Cisco simulations, SIEM implementation

Information Technology Intern

Aug 2024 – Sep 2024

National Bank of Egypt (NBE), Cairo, Egypt (Internship, On-site)

  • Gained hands-on experience in IT operations, software testing, and troubleshooting

Internship Trainee

Jul 2024 – Aug 2024

Commercial International Bank Egypt (CIB), Giza, Egypt (Internship, Online)

  • Explored banking operations, teamwork, and industry practices through a structured program

Projects

DroneSentinel: AI-Based Security Gap Monitoring System

DroneSentinel Project
  • Graduation Project - Specialized AI-based drone detection system
  • Focused security gap monitoring (not general detection)
  • Three security gaps: Radar overhead blind spot, Perimeter chokepoints, Visual verification
  • Uses YOLOv8 + BoT-SORT for advanced tracking and analytics
  • AES-256 encryption, secure authentication, audit trails
  • Real-time alerts, multi-channel notifications, performance analytics
  • Cost-effective alternative to human guards (90% savings)

IoTCPS-AI-IDS: AI-Based Intrusion Detection System

IoT AI IDS System
  • Deep learning-based Intrusion Detection System for IoT Cyber-Physical Systems
  • Achieves 99.6% accuracy detecting IoT network attacks
  • Detects Mirai botnet, DoS, MITM, and scanning attacks
  • Real-time detection with TensorFlow backend
  • Includes model serialization, preprocessing pipeline, and evaluation tools
  • Trained on IoTID20 dataset (3.2 million network flows, 85+ features)

⭐ ExeRay – AI-Powered Malware Detection (Most starred and forked repository on my GitHub)

ExeRay AI-powered malware detection project
  • Developed machine learning system to detect malicious .exe files
  • Analyzes static features (entropy, imports, metadata)
  • Combines Random Forest/XGBoost AI models with heuristic rules
  • Provides fast, accurate classification
  • Reduces reliance on signature-based detection
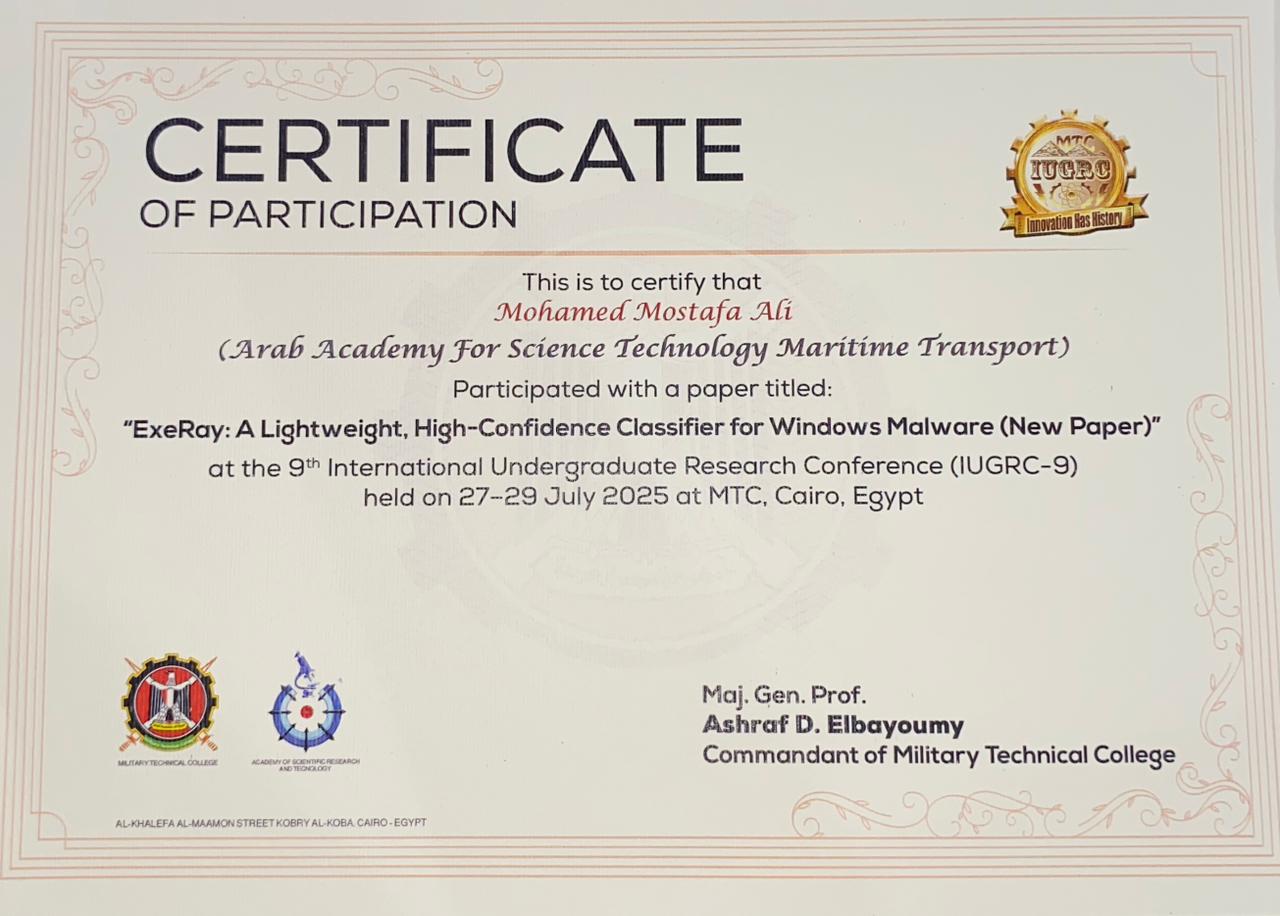
  • Presented the ExeRay scientific research paper at the 9th International Undergraduate Research Conference (IUGRC 2025), held at the Military Technical College (MTC), Cairo, Egypt.
  • The full academic paper (PDF) is included in this repository (Click on Github icon) under the assets/ folder: ExeRay Paper.pdf

Metasploitable 2 Security Assessment – 46 Findings Report

Metasploitable 2 security assessment report
  • Comprehensive penetration testing report against Metasploitable 2 VM
  • Identified 46 security findings across network services and web applications
  • Covered Network Services (17), Web Applications (22), Privilege Escalation (4), Enumeration (3)
  • Tools used: Metasploit, Nmap, Nikto, SQLMap, manual exploitation
  • Team-based project simulating real-world healthcare IT infrastructure testing

Conpot ICS Honeypot Analysis

Conpot ICS Honeypot
  • Industrial Control Systems (ICS) honeypot deployment using Conpot
  • Simulates realistic industrial protocols (Modbus, S7Comm, BACnet, SNMP)
  • Captures attacker reconnaissance behavior and ICS-targeted threats
  • Analysis using Nmap, Wireshark, and traffic capture tools
  • Documented attacker interaction patterns and tool behaviors
  • Critical for infrastructure security in energy, water, and manufacturing

MISP Threat Intelligence Journey

MISP Threat Intelligence
  • Comprehensive exploration of MISP (Malware Information Sharing Platform)
  • Threat intelligence platform setup and configuration
  • Analysis of IOC (Indicators of Compromise) sharing and collaboration
  • Integration with other security tools and platforms
  • Real-world threat intelligence workflows and best practices

Self-Initiated Cloud-Based SSH Honeypot with AbuseIPDB Integration

SSH honeypot with AbuseIPDB integration project
  • Developed low-interaction SSH honeypot deployed on Azure using Terraform
  • Designed to log unauthorized access attempts and analyze attack patterns
  • Integrated AbuseIPDB with SSH honeypot tool Pshitt
  • Provides real-time IP reputation checks and automated reporting
  • Detailed logging of attack sources, credentials, and metadata

Self-Initiated Sliver C2 & Botnet Small Lab: Cloud-Based Red Teaming

Sliver C2 and botnet cloud lab project
  • Built cloud-based red teaming practice lab using Azure and Terraform
  • Experimented with infrastructure as code (IaC) and automated deployments
  • Lab consists of C2 machine and botnet of two compromised VMs
  • Utilized Sliver framework for command and control
  • Analyzed traffic using Wireshark for C2 communications insight
  • Gained hands-on experience in post-exploitation and lateral movement

TuxTrace – Forensic Artifact Generation Tool

TuxTrace forensic artifact generation tool
  • Built Python-based tool to simulate activity for multiple users
  • Each user has unique profiles generating realistic forensic artifacts
  • Generates .bashrc, .bash_history, auth.log, /tmp files, and Cron jobs
  • Dockerized for easy deployment in training and forensics labs

University Financial System Threat Modeling and Security Testing Using MTM 2016

University financial system threat modeling project
  • Conducted comprehensive threat modeling for a university's financial system
  • Focused on securing Kerberos-based authentication
  • Designed Data Flow Diagram (DFD) and identified 113 threats with 85% mitigation
  • Developed attack tree validated against MITRE ATT&CK framework

Decentralized IoT Authentication on Ethereum

IoT Authentication Smart Contract
  • Solidity smart contract for secure IoT device authentication on Ethereum blockchain
  • Features device registration/deregistration (owner-only)
  • Secure data recording using hashed payloads with replay attack protection
  • Event-based logging for full transparency and audit trails
  • Paris EVM compatible (post-Merge Ethereum)
  • Provides decentralized authentication and data integrity for IoT devices

System Performance Monitor Project with Bash and Docker

Docker system performance monitor project
  • Developed containerized system monitoring script using Docker
  • Provides dynamic and efficient performance insights
  • Monitors system metrics and displays real-time statistics
  • Utilizes shell scripting and container orchestration techniques
  • Overcame challenges related to runtime configurations
  • Ensured compatibility with modern GPU-based environments

Certificates

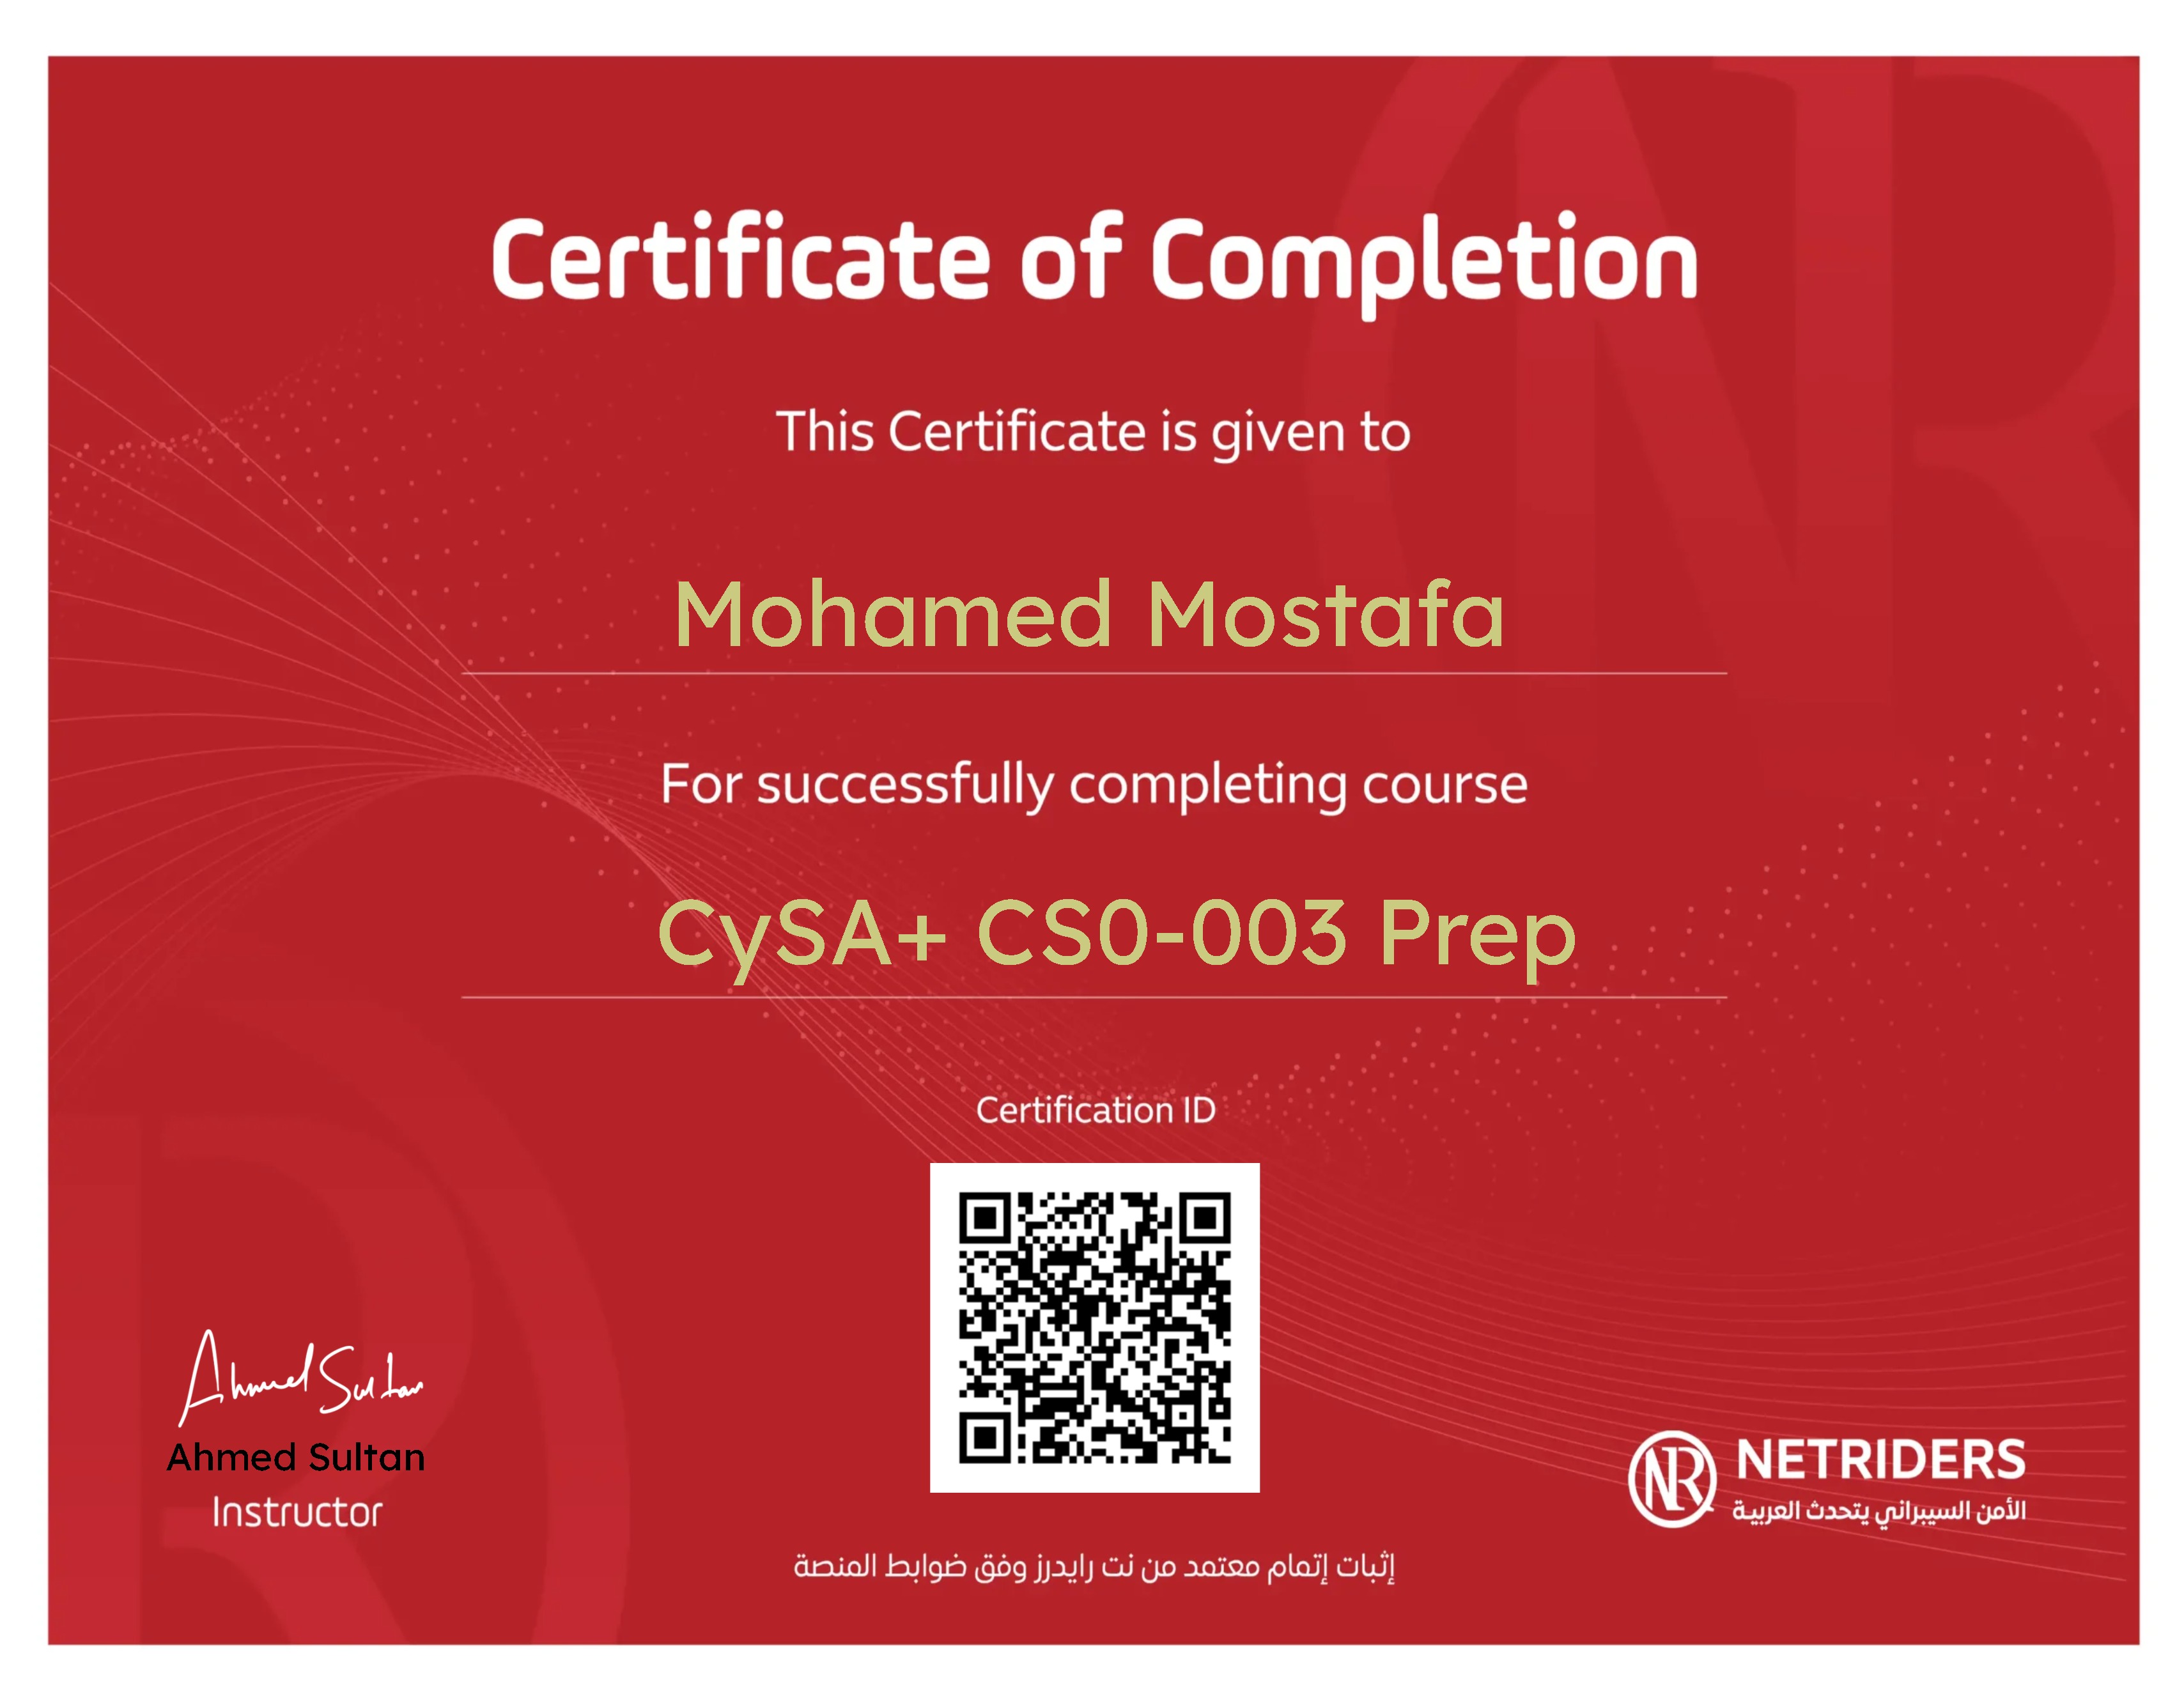
CompTIA CySA+ certificate
CompTIA CySA+
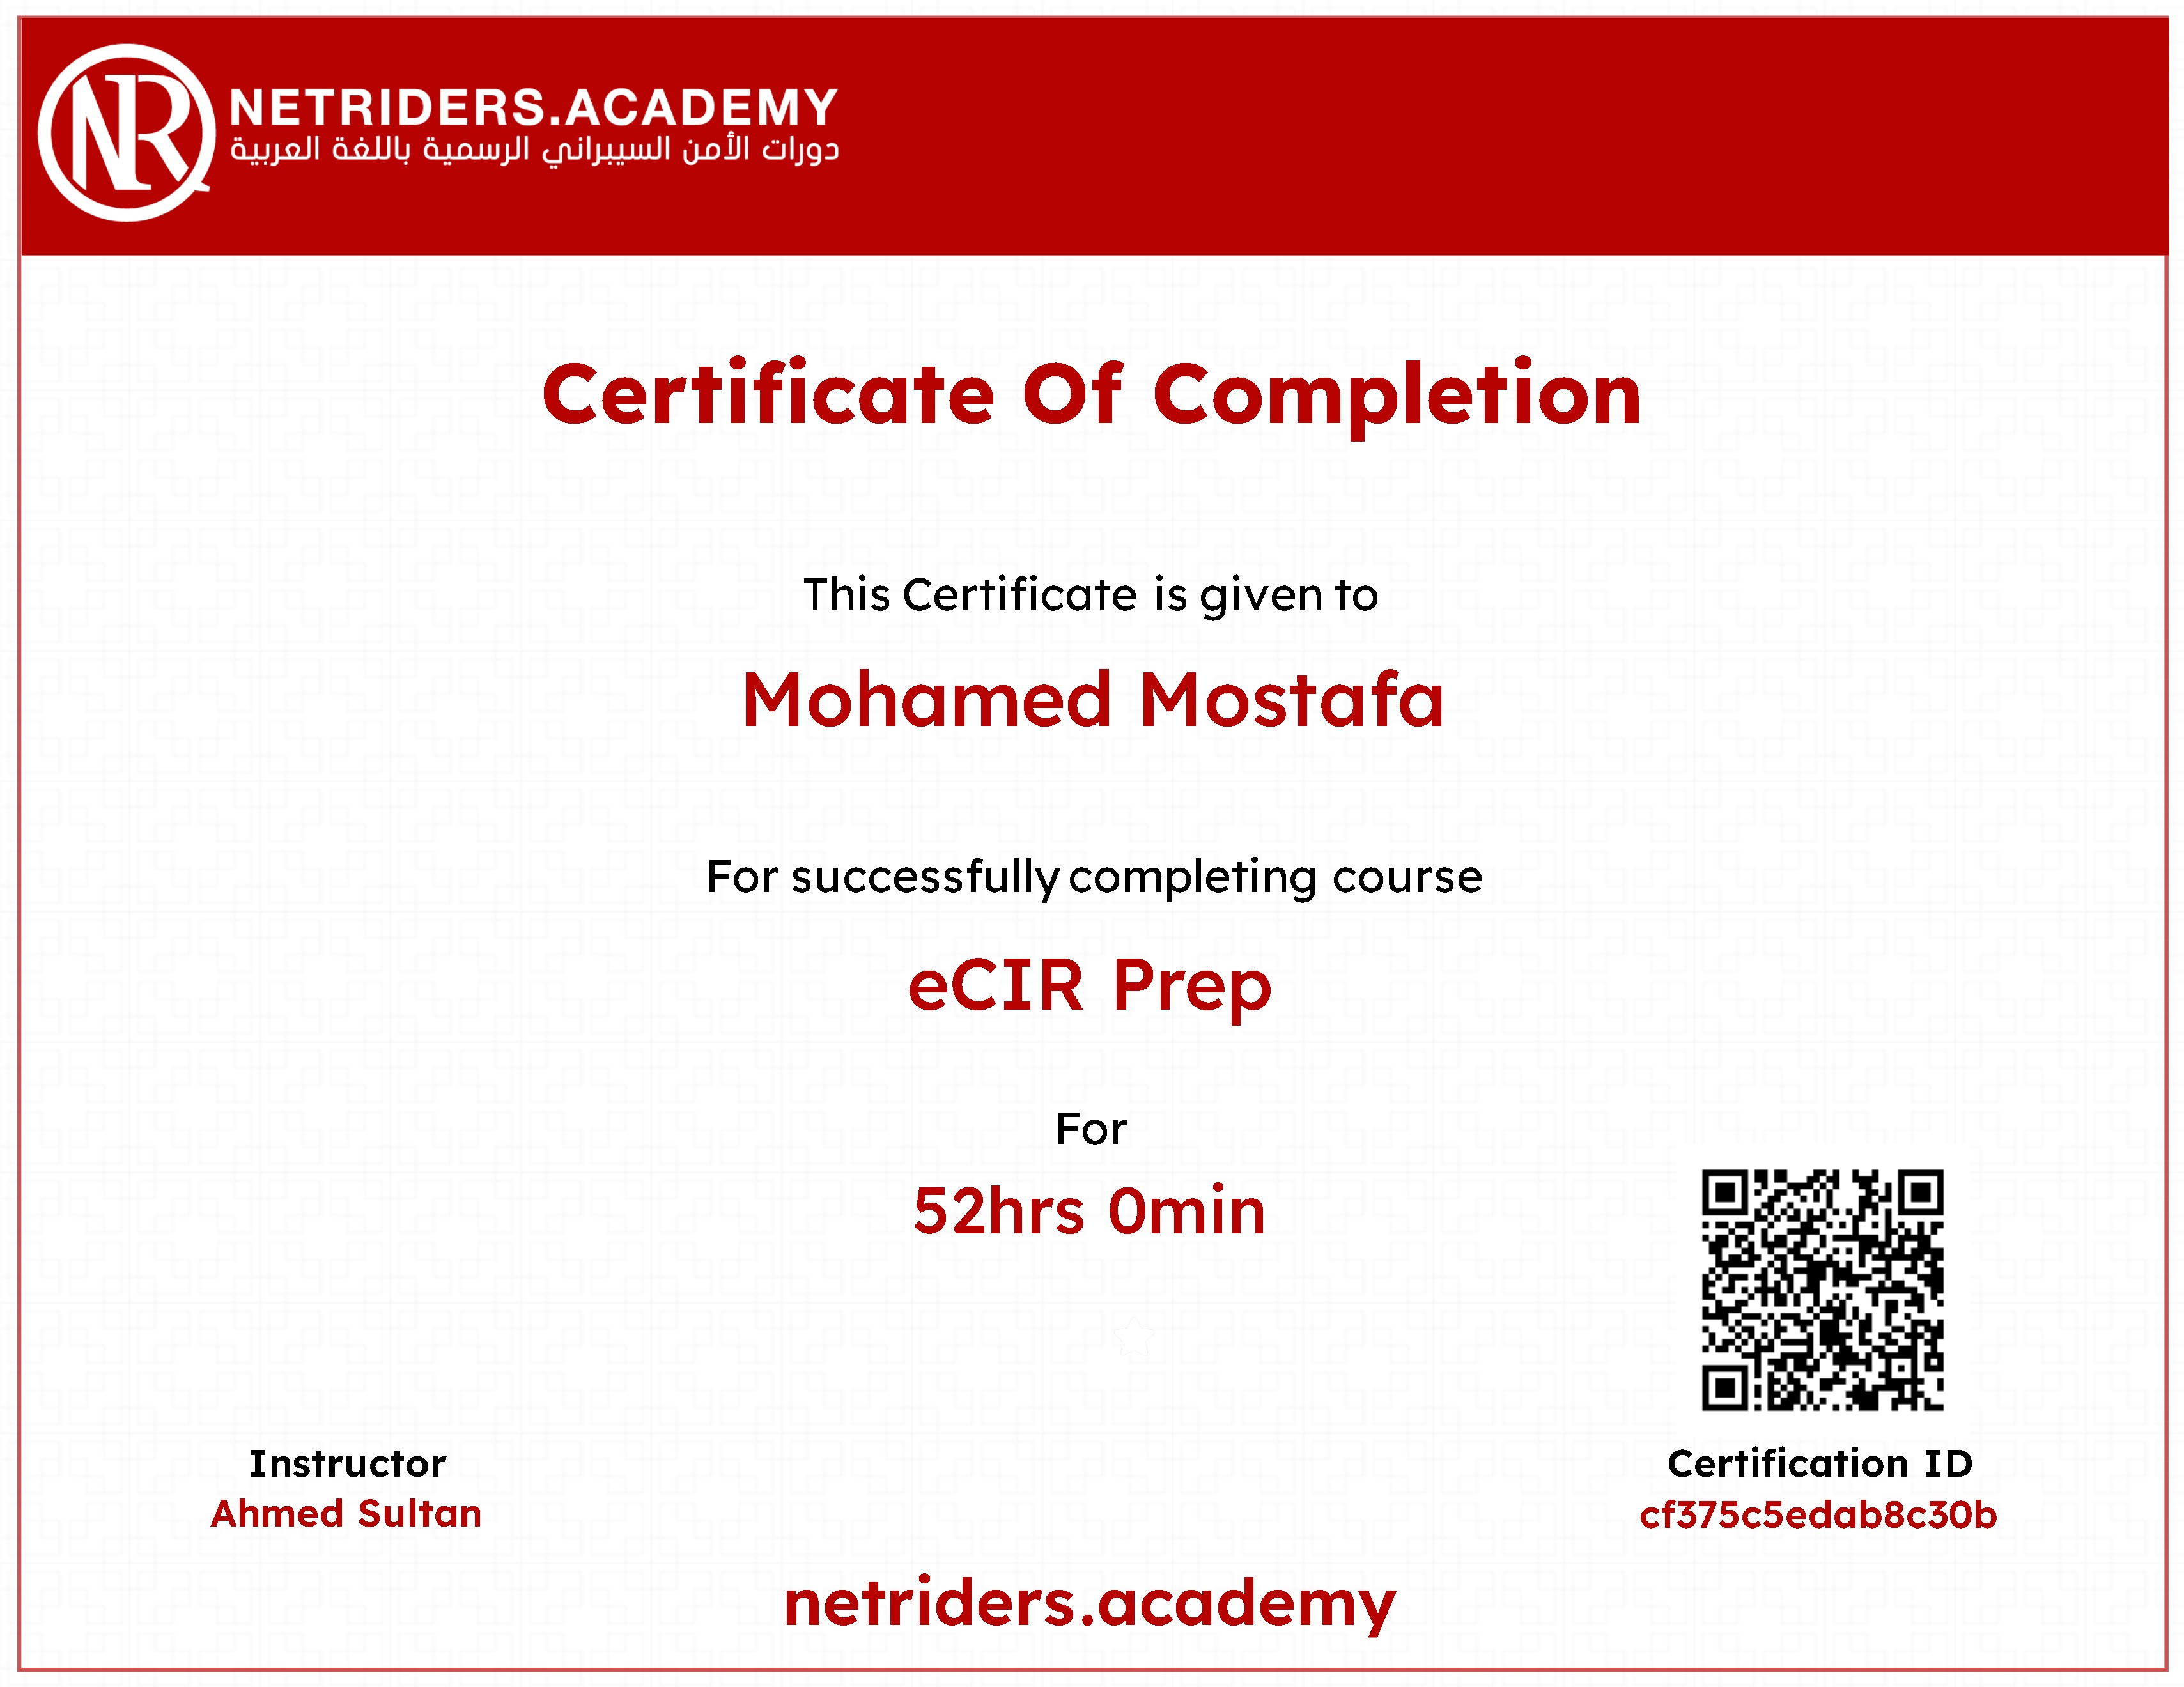
eCIR – Certified Incident Responder certificate
eCIR – Certified Incident Responder
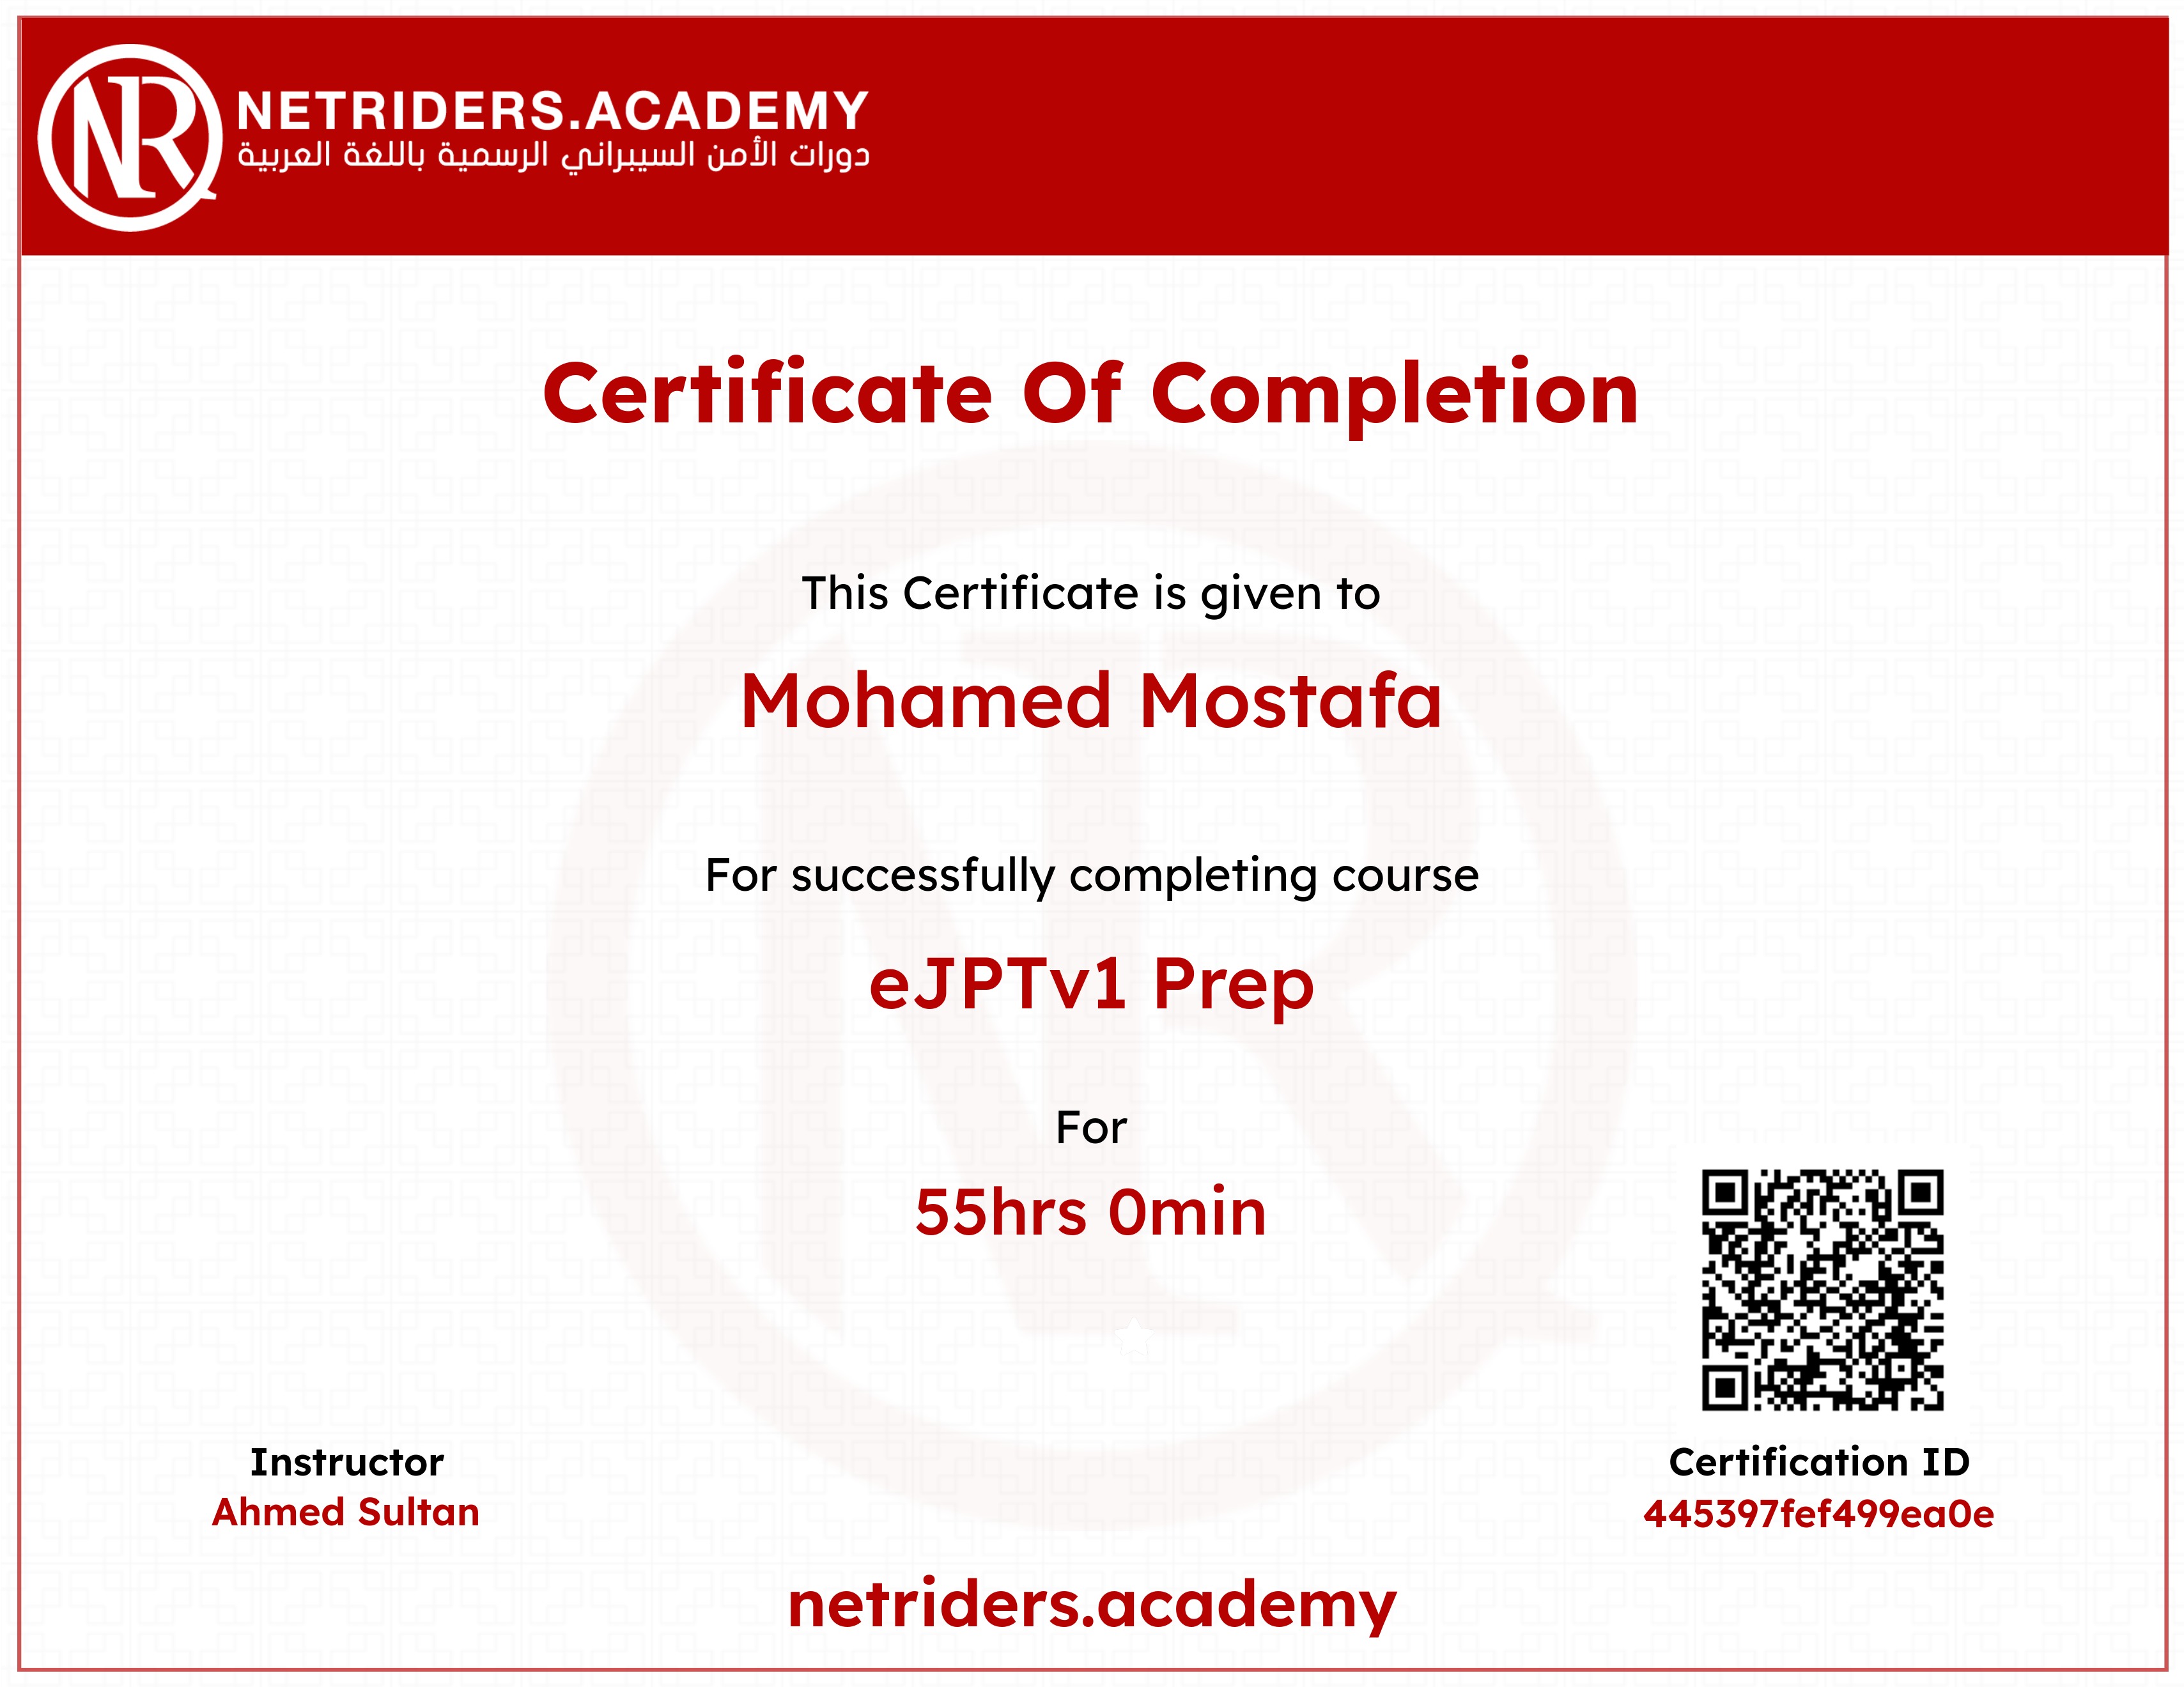
eJPTv1 – Junior Penetration Tester certificate
eJPTv1 – Junior Penetration Tester
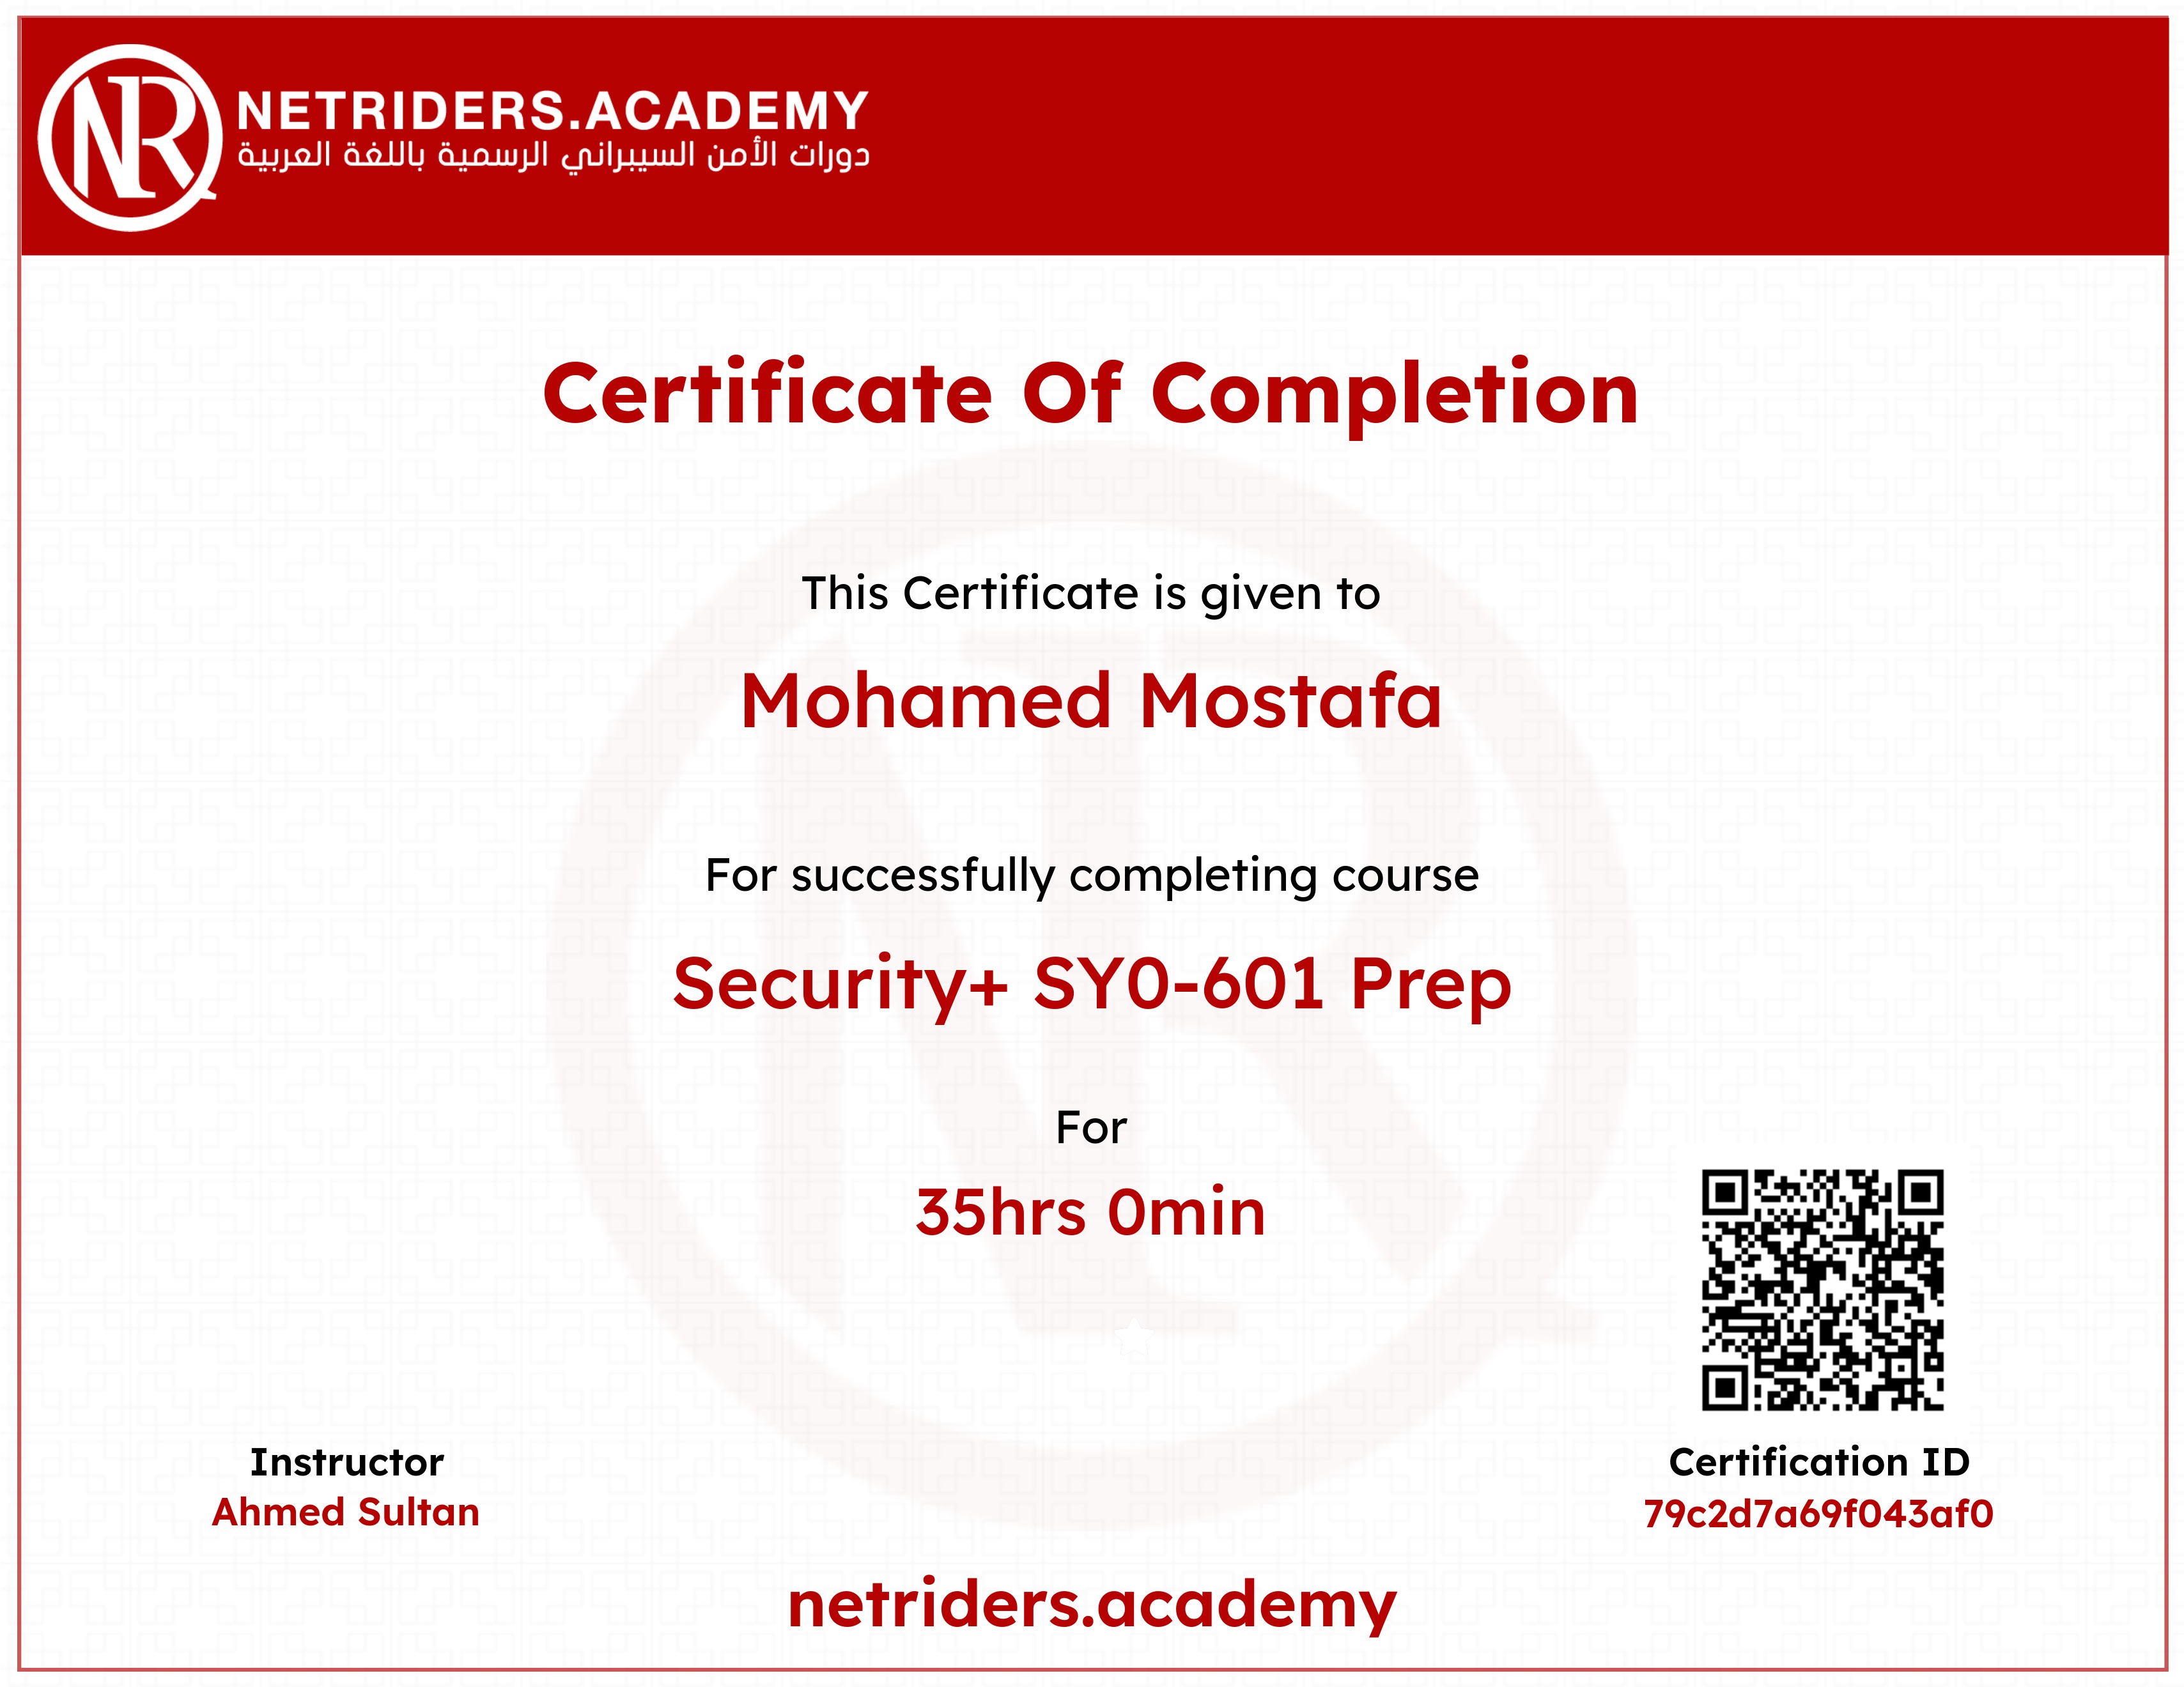
CompTIA Security+ certificate
CompTIA Security+
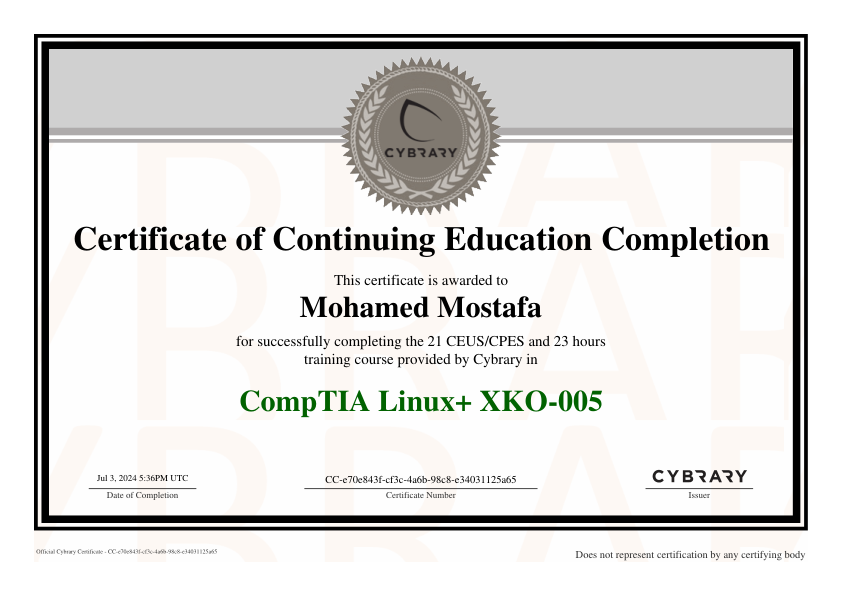
CompTIA Linux+ certificate
CompTIA Linux+
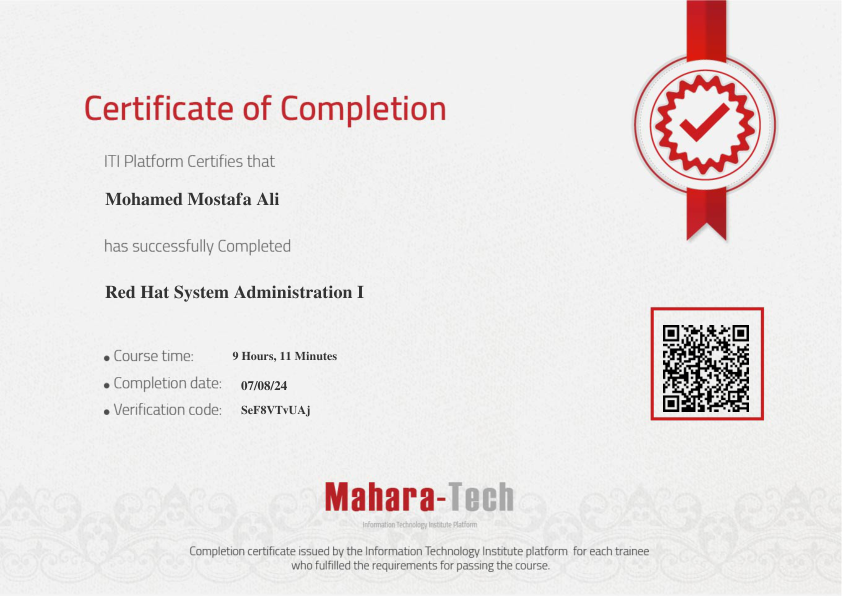
Red Hat System Administration certificate
Red Hat System Administration
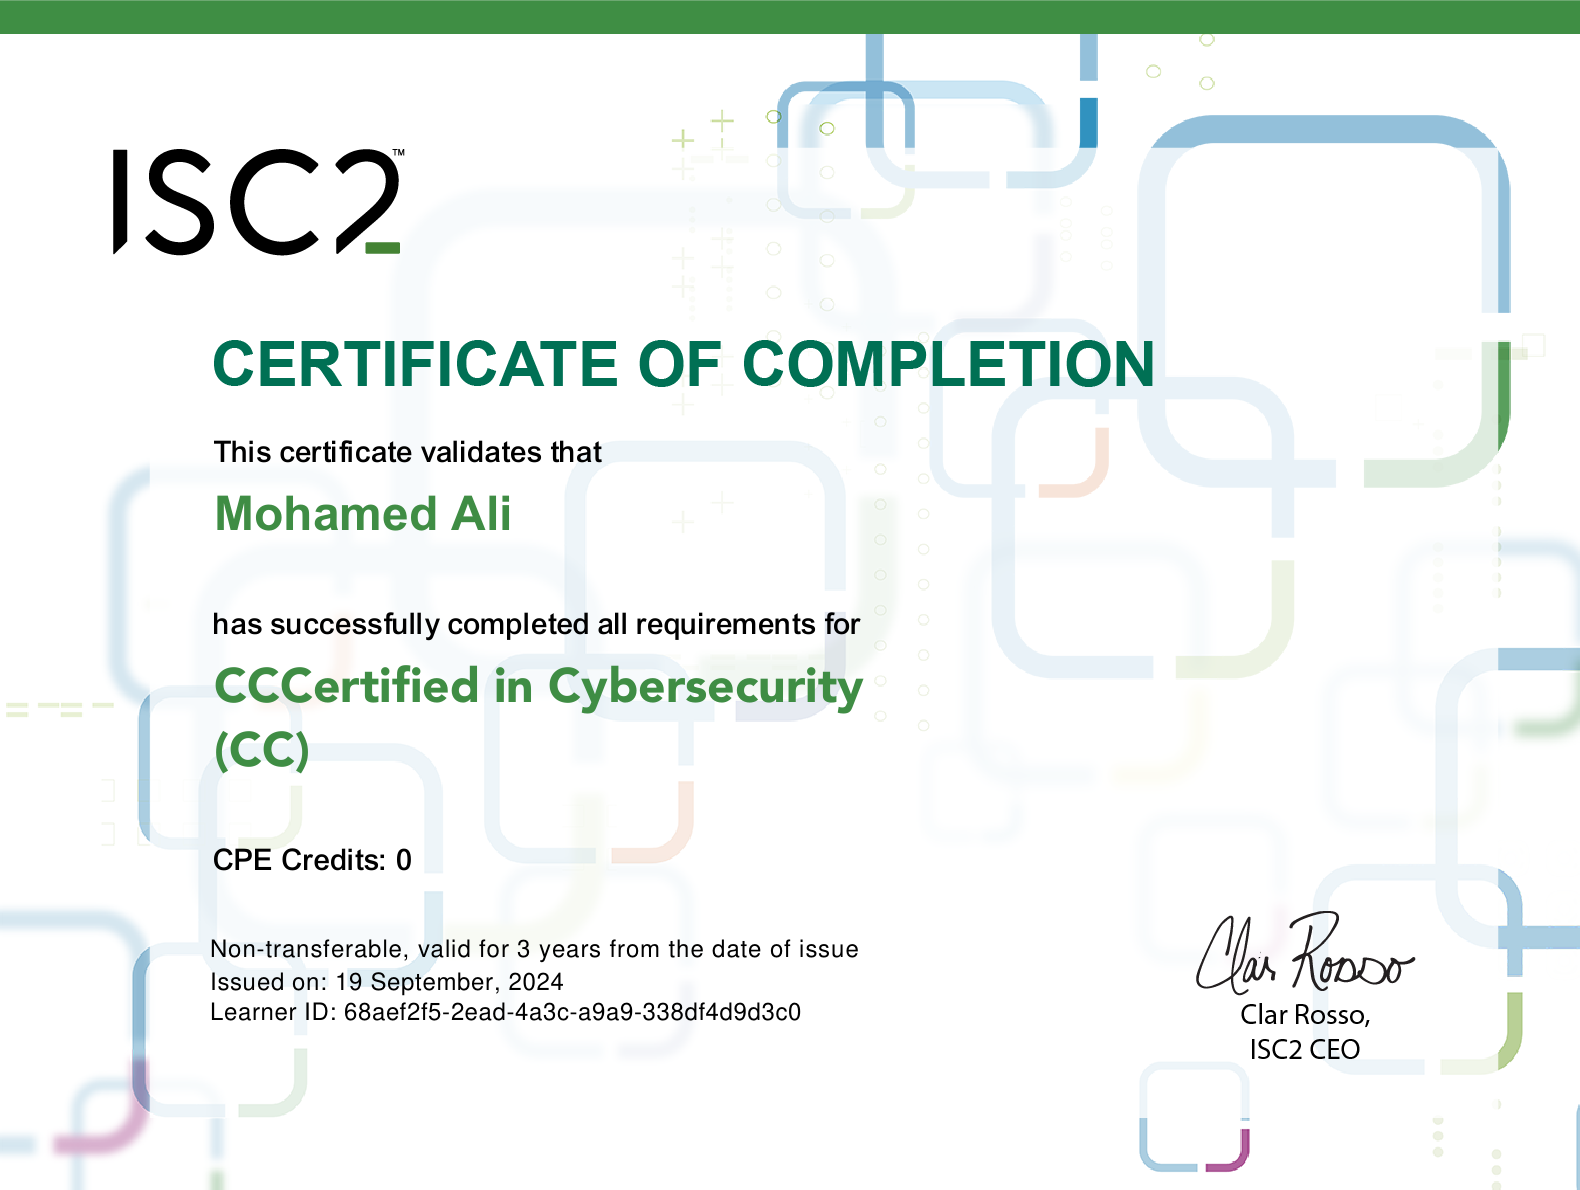
(ISC)² Certified in Cybersecurity certificate
(ISC)² Certified in Cybersecurity
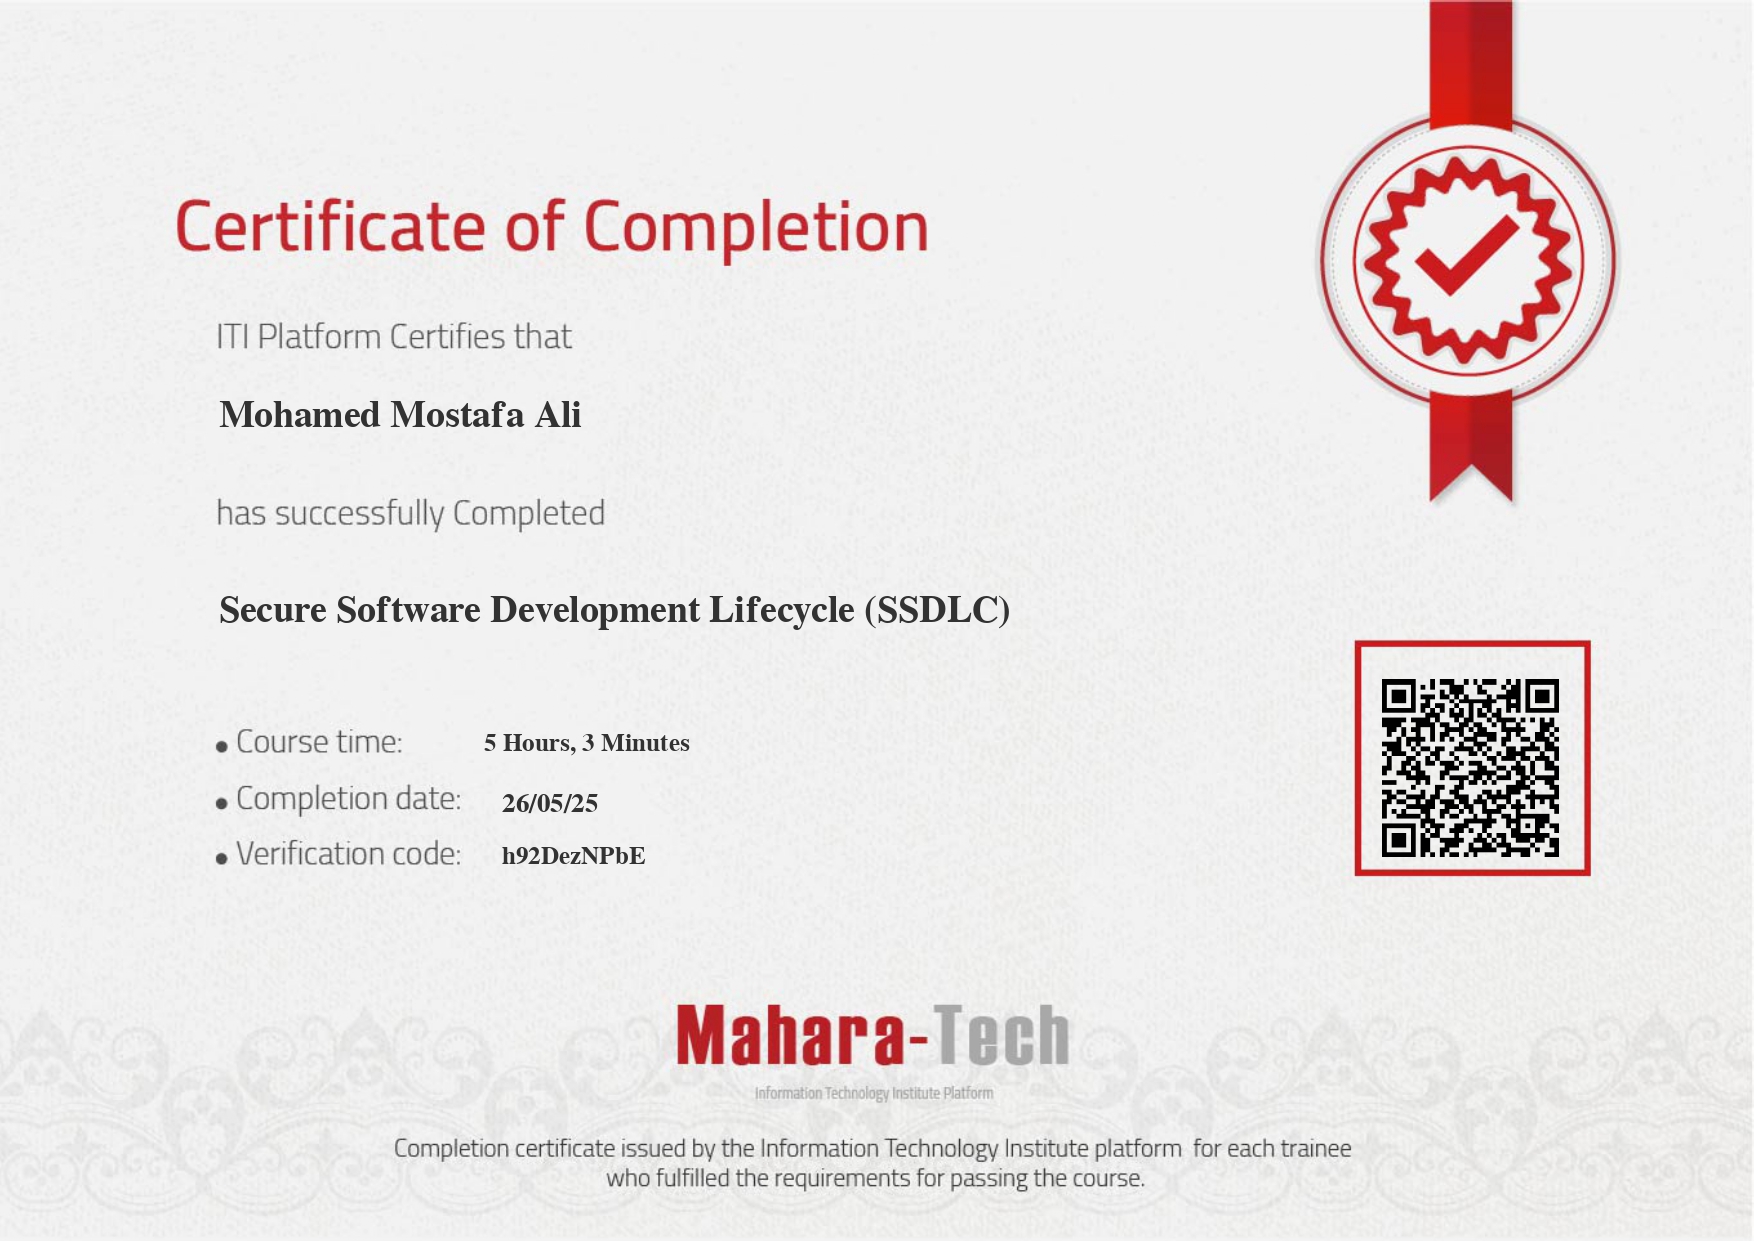
Secure Software Development Lifecycle certificate
Secure Software Development Lifecycle
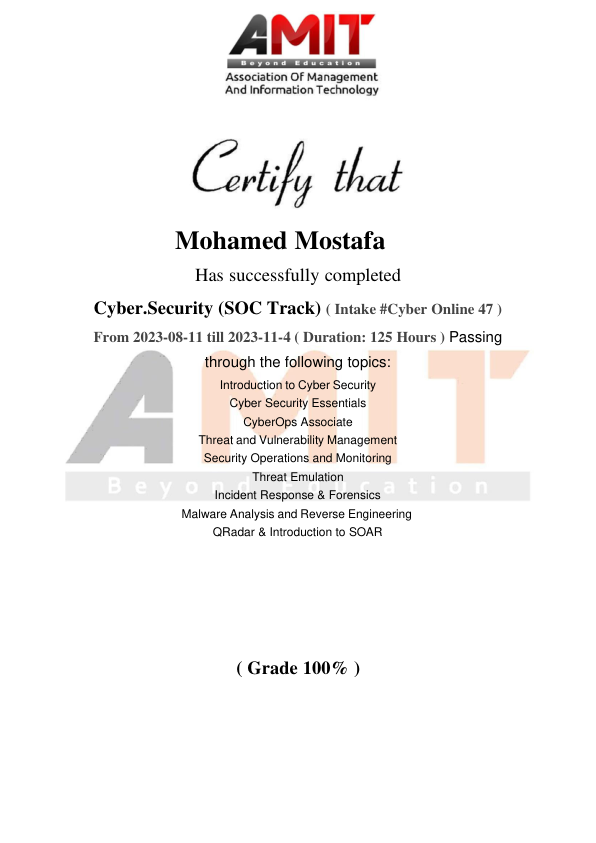
AMIT SOC Diploma certificate
AMIT SOC Diploma
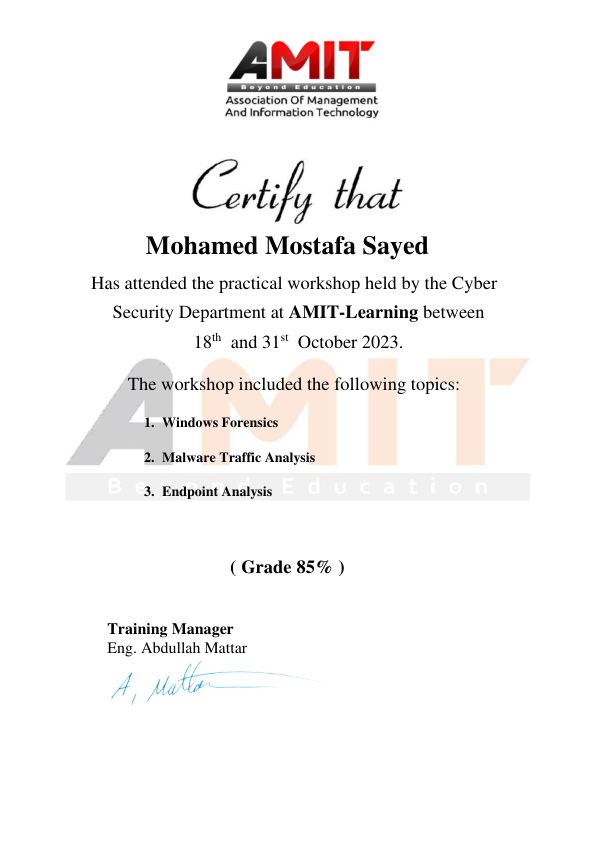
AMIT Workshop certificate
AMIT Workshop
IUGRC 2025 – Research Presentation certificate
IUGRC 2025 – Research Presentation
TryHackMe learning path certificate 1
TryHackMe Learning Path
TryHackMe learning path certificate 2
TryHackMe Learning Path
TryHackMe learning path certificate 3
TryHackMe Learning Path
TryHackMe learning path certificate 4
TryHackMe Learning Path
TryHackMe learning path certificate 5
TryHackMe Learning Path
TryHackMe learning path certificate 6
TryHackMe Learning Path

Contact Me